For entities included in the NIS list in 2025, the deadline to adopt basic security measures falls in October 2026, 18 months after receiving the ACN communication. There is no single deadline of October 31: each entity must verify the date of its own communication. Having a risk analysis, an incident management policy, and a business continuity plan is not enough if the planned measures are not adopted. The measures must be adopted in practice: policies and documents help, but alone are not sufficient to demonstrate their implementation.
Legislative Decree 138/2024 transposes the NIS2 directive in Italy. The basic specifications published by ACN indicate the measures to be adopted, with deadlines linked to the inclusion communication. A company might have written a perfect access management plan and continue to share credentials on a company chat. In an audit, policies and evidence of their implementation can be examined together: logs and records help reconstruct the activities performed.
What changes in October 2026
For entities included in the list in 2025, the obligation to report basic significant incidents is operational from January 2026. Basic security measures, however, must be adopted within 18 months of the inclusion communication: for many, the deadline falls in October 2026, but the specific day depends on the communication received. For entities included for the first time in 2026, ACN indicates different deadlines, including July 2027 for basic measures. Consult the ACN communication on new entities.
The annexes of ACN determination 379907/2025 distinguish basic measures for essential and important entities. They concern risk management, supply chain security, incident management, and access control. But beneath every measure there is the same question: if an inspector asked for proof, would you be able to retrieve it from emails, shared folders, and files on different computers?
Measures, audits, and penalties
Penalties are regulated by article 38 of Legislative Decree 138/2024. The application of penalties depends on the violation ascertained, the category of the entity, and the circumstances provided for by the decree. A document platform does not replace the assessment of obligations nor does it prevent penalties.
During an audit, documents and evidence pertinent to the adopted measures may be requested. Access logs and version history can help reconstruct document management. If the answer is to search through different people's mailboxes, the problem is not abstract cybersecurity: it is that the documents demonstrating the work done are scattered, without a consistent record of who touched them.
Why the document archive is a hole almost no one looks at
NIS2 measures also concern risk and incident management. Document traceability can provide useful evidence: where are the previous versions of a security plan updated three times in a year, who shared that report with an external supplier, when was a certain register last opened.
For a company that manages these documents in generic shared folders, reconstructing that history in October, under inspection, is a manual, slow, and often incomplete task. An archive that automatically tracks versions, accesses, and shares makes it easier to consult the available history. It does not replace risk analysis or the policies that a company must still write: it can provide useful evidence to support the verification of adopted measures, without by itself demonstrating compliance with NIS2 obligations.
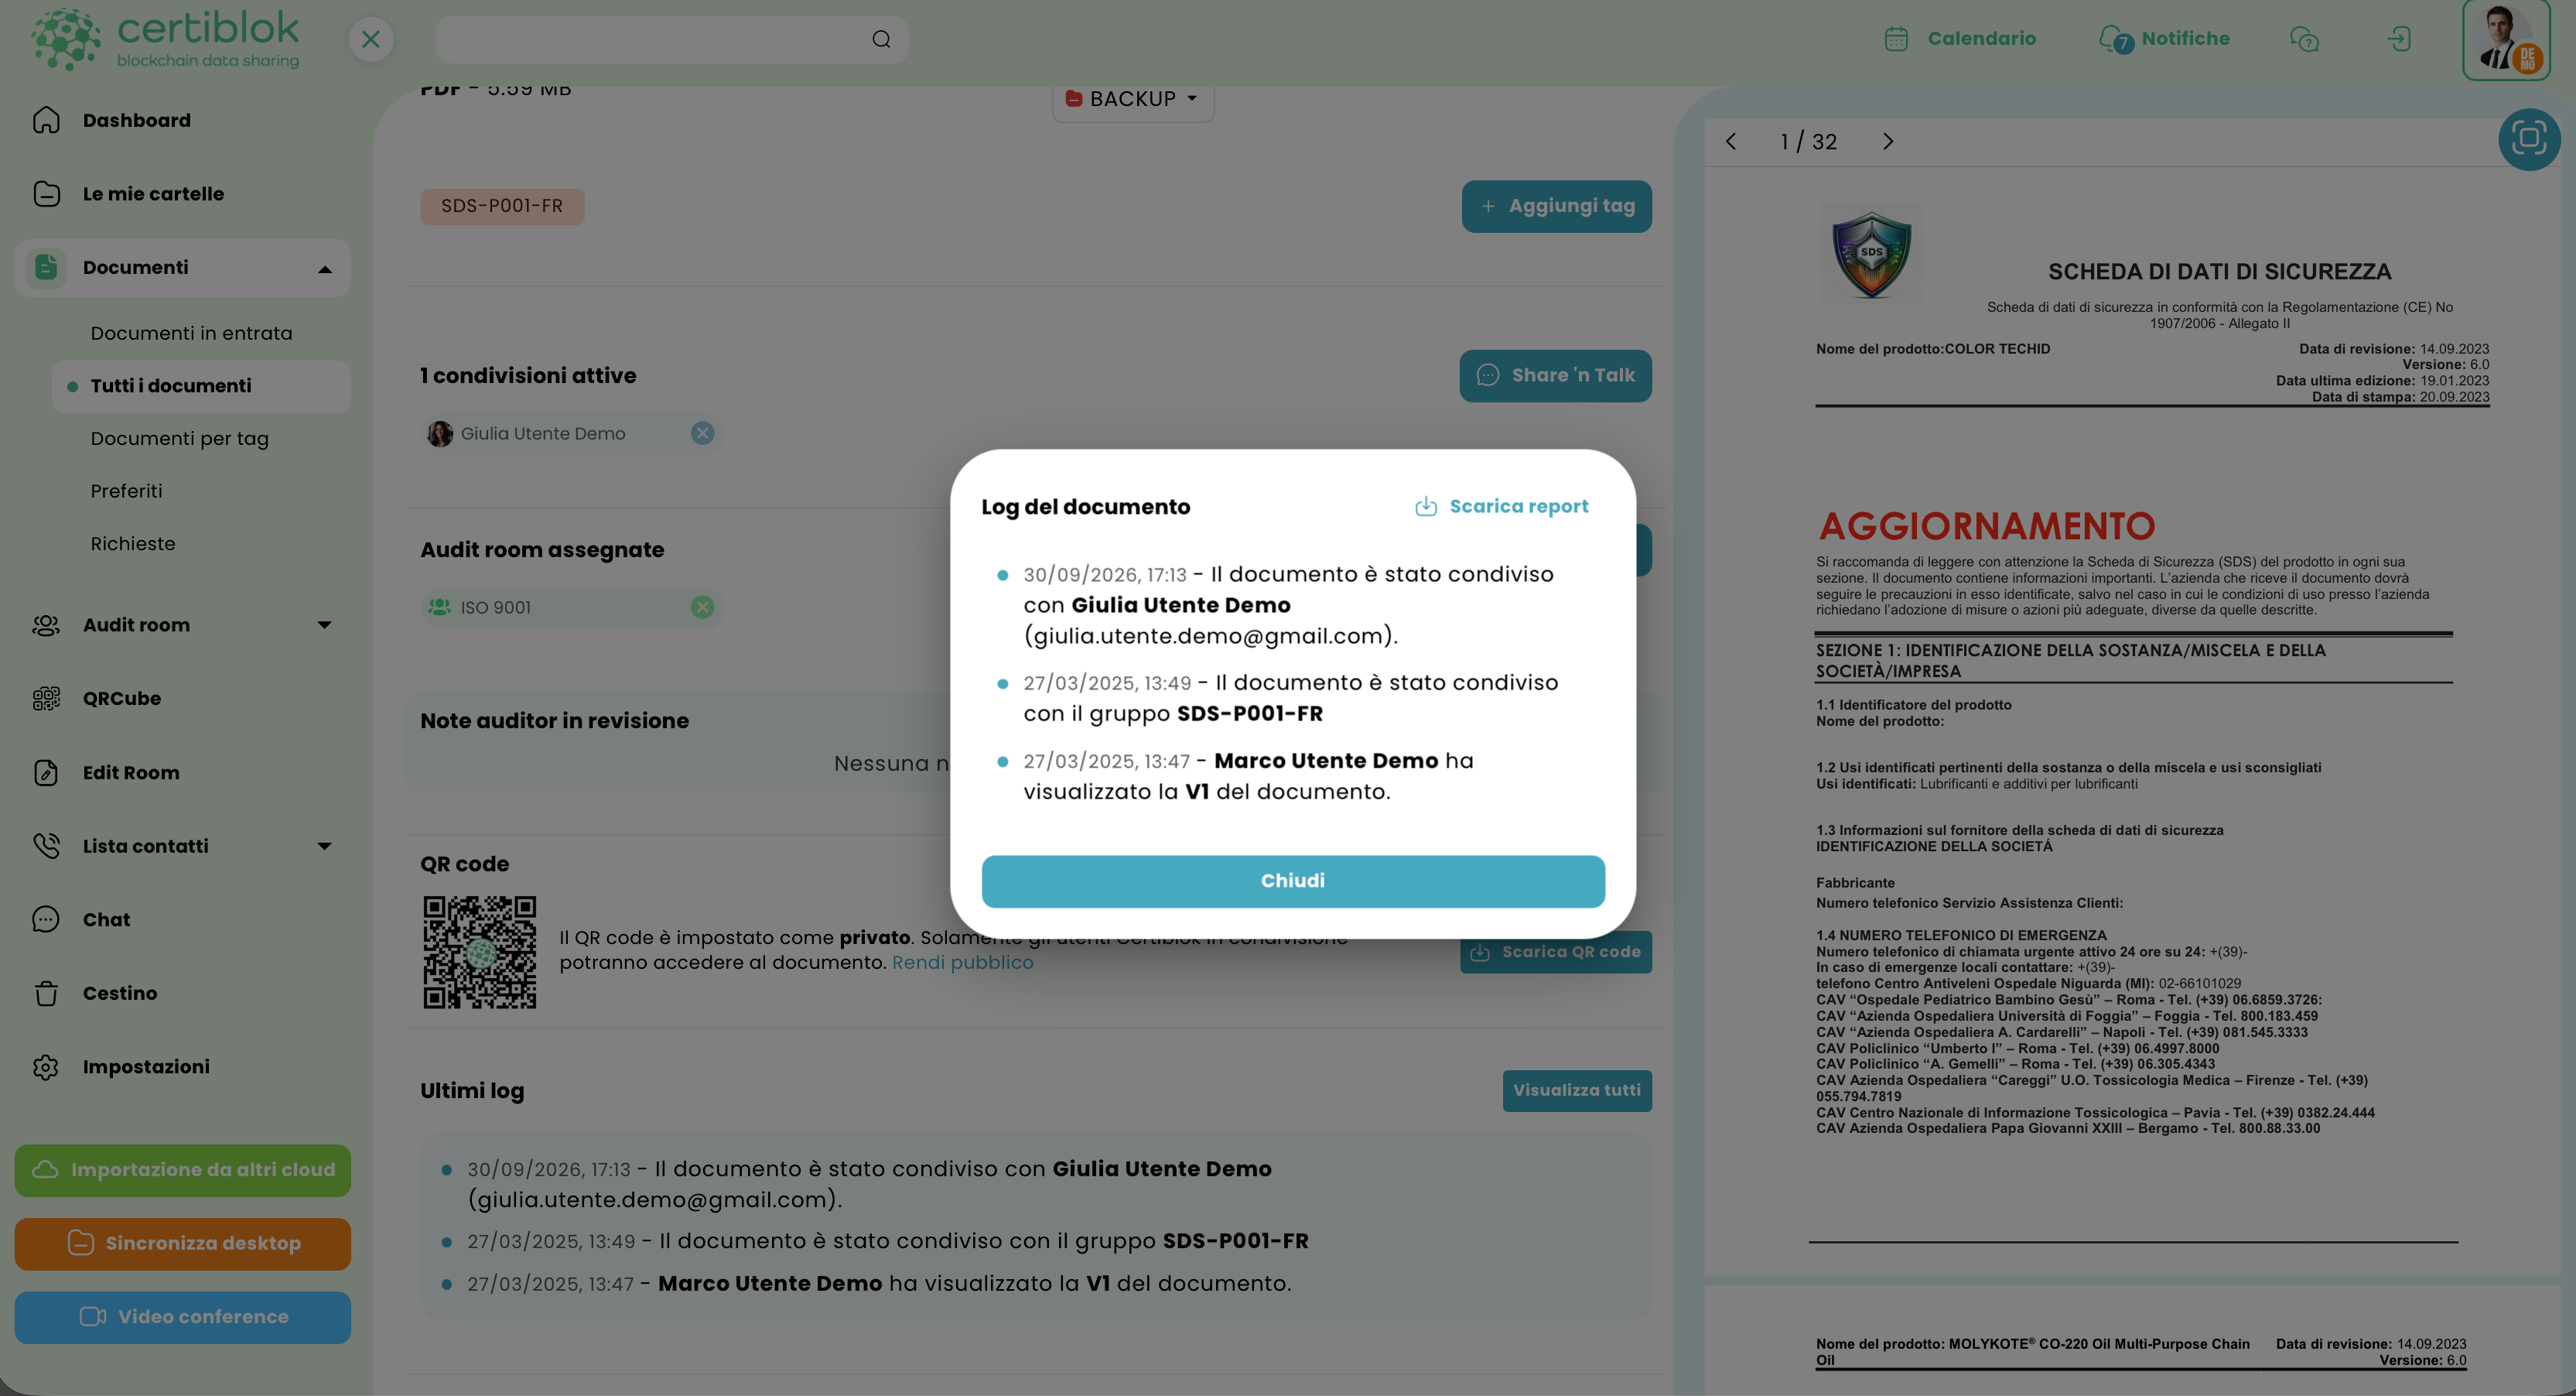
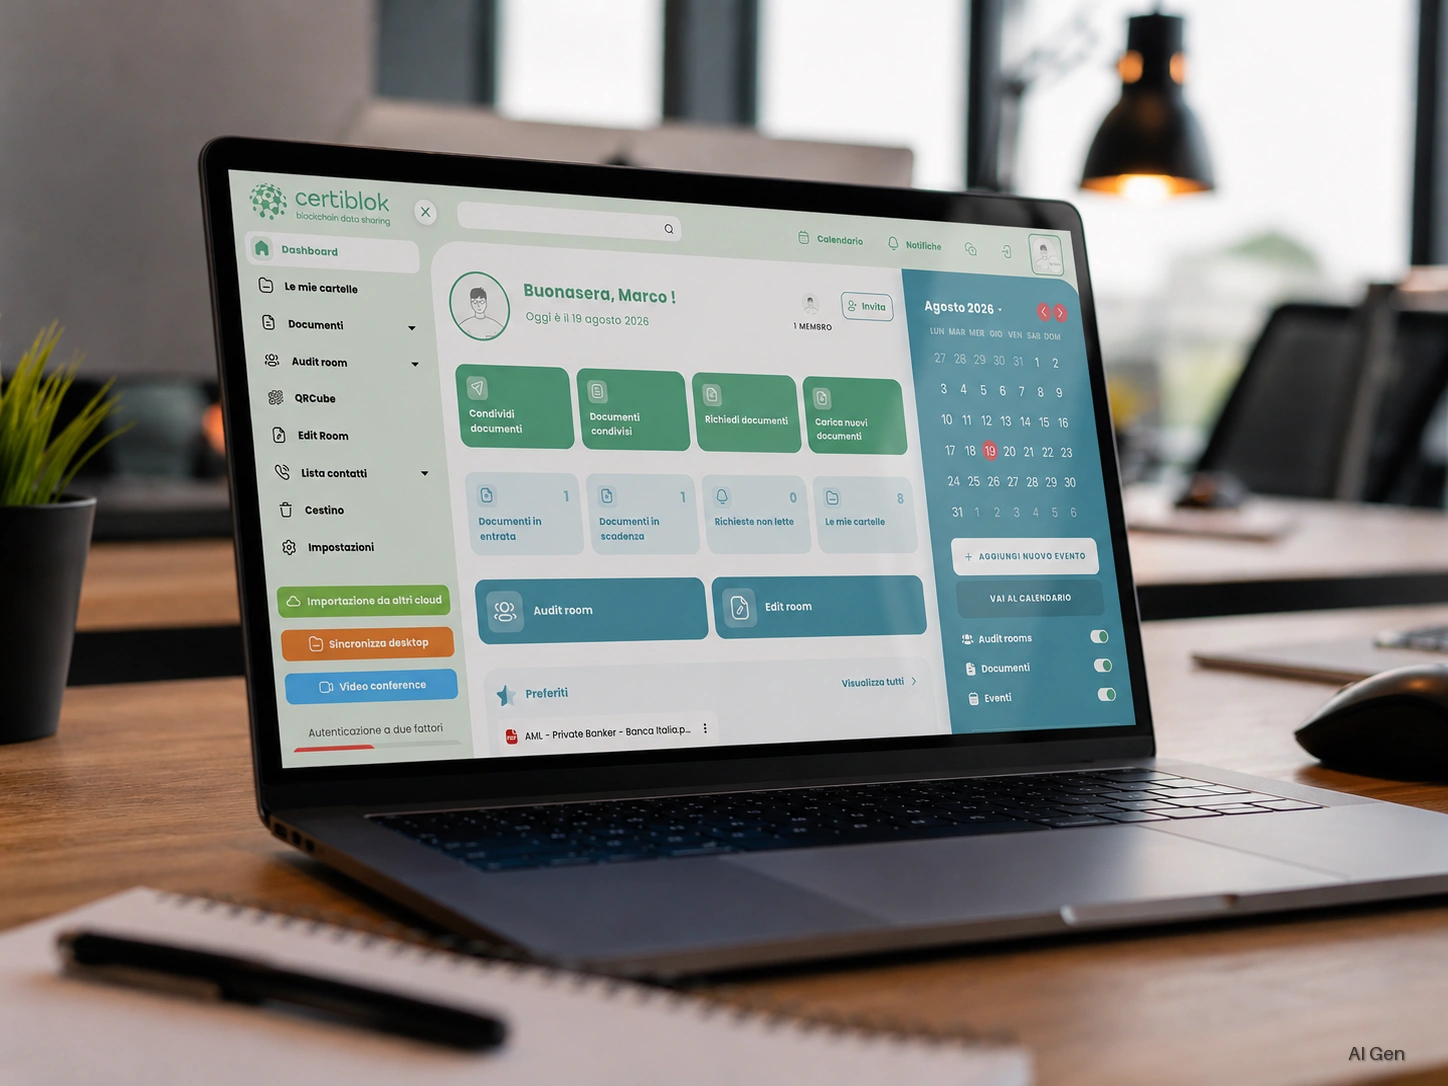
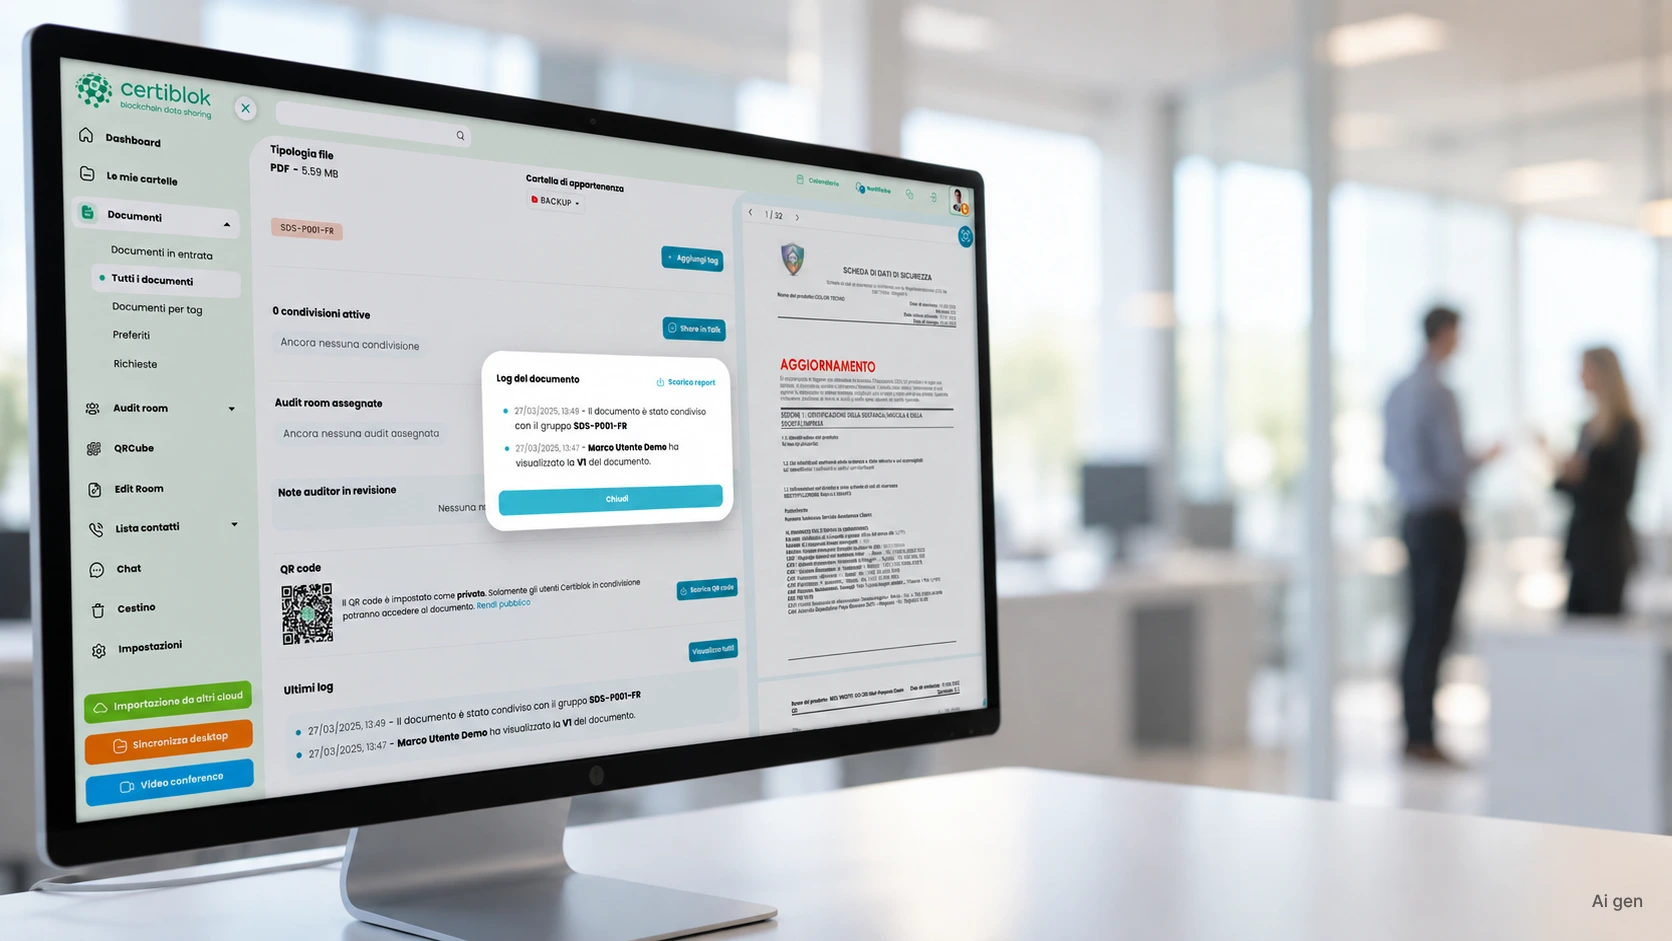
Certiblok®, with the DRM® & Archive module, maintains the history of every document version with date, time, and who modified it, and a log of every access. The Audit Room allows an inspector to access a document room limited to only pertinent files, without handing over company credentials. These elements help produce the required evidence: compliance with NIS2 obligations remains a company's responsibility, not something a document platform alone can guarantee.
What to do before your deadline
Those who fall into the first NIS group must verify the date of their ACN communication and whether basic measures have been adopted. Documentary evidence aids verification but does not replace security measures. It is worth asking, for each of the areas required by Legislative Decree 138/2024: if an inspector asked today, who in the company would be able to quickly retrieve the proof, and from where.
For the general overview on NIS2 and GDPR, read what you truly risk in case of a cyber attack. Learn more about Certiblok®'s UNI CEI EN ISO/IEC 27001:2024 certified information security management system and the DORA framework for the financial sector: these are distinct topics, not shortcuts to comply with NIS2.


